Underline the functional distinction between CERT-In and NCIIPC under the IT Act. How does this institutional division strengthen India’s proactive cyber-incident response mechanism?
CERT-In and NCIIPC are both key cyber-security institutions under the IT Act, but they serve different purposes. CERT-In is the national nodal agency for handling cyber incidents across the wider digital ecosystem, while NCIIPC focuses only on Critical Information Infrastructure whose disruption can affect national security, economy, public health or safety.
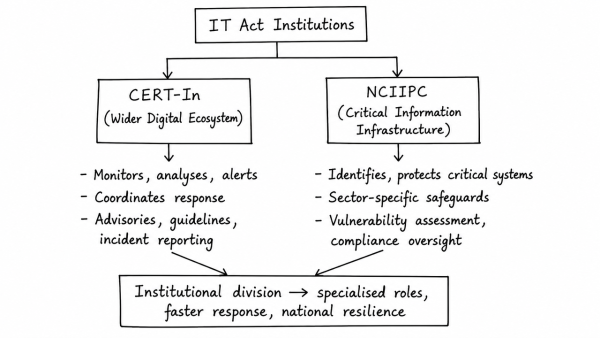
- CERT-In: monitors, analyses and issues alerts on cyber incidents; coordinates emergency response; provides advisories, guidelines and incident reporting directions for service providers, intermediaries and body corporates.
- NCIIPC: identifies and protects critical systems; frames sector-specific safeguards; oversees vulnerability assessment, compliance and strategic protection of CII.
This division strengthens proactive response in two ways: first, it avoids a one-size-fits-all approach by separating mass cyber hygiene from high-value infrastructure defence. Second, it enables faster warning, clearer accountability and specialised protection for vital networks. Together, they create a layered system of early detection, rapid response and targeted resilience.
Originally written on
August 10, 2026
and last modified on
September 24, 2026.